PHP2Shell: what it means for MapStore, GeoServer and GeoNode users
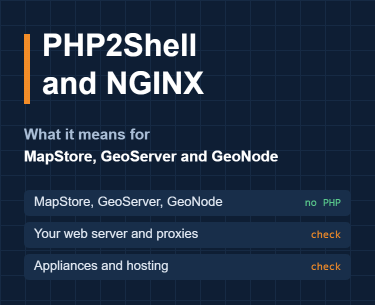
On 21 October 2026 the PHP project released fixes for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, now known as PHP2Shell. They allow unauthenticated remote code execution on web servers running PHP. Exploitation attempts were observed even before public disclosure. The UK NCSC has issued an alert asking organisations to find and patch every PHP installation, and to take offline what they cannot fix.
Since then we have been receiving questions from organisations running our open source products. Here is the short answer, and what we suggest you check.
Are MapStore, GeoServer and GeoNode affected?
No since none of them uses PHP.
- MapStore is a Java web application. Its frontend is JavaScript running in the browser.
- GeoServer is a Java web application.
- GeoNode is a Python (Django) application, with GeoServer as its map server.
The official distributions and Docker images do not include or depend on PHP. PHP2Shell is not relevant to MapStore, GeoServer or GeoNode as released.
Your installation is a different question
The products are not affected, but your deployment might still be exposed. Every installation is different, and we usually have no visibility on how yours was set up. So take a look at the whole stack around your maps.
- Web servers and reverse proxies. MapStore, GeoServer and GeoNode are often published behind Nginx or Apache httpd. Nginx and Apache are not affected by PHP2Shell on their own, but the same server often also hosts PHP applications through PHP-FPM or mod_php. Check what else runs there. Nginx itself needs attention too: on 21 October 2026, the same day as PHP2Shell, F5 disclosed three critical Nginx vulnerabilities (CVE-2026-15176, CVE-2026-97205, CVE-2026-93479), after NGINX Rift (CVE-2026-42945) in May. If you run Nginx in front of your maps, including as a container in Docker based deployments, update it to the latest security release.
- Other applications on the same hosts or network. Content management systems, intranet portals and websites embedding your maps are often PHP based. WordPress, Drupal, Joomla and Moodle are all PHP.
- Appliances and third party products. PHP is embedded in many products, including some firewalls and VPN gateways. Follow your vendors’ advisories.
- Hosting providers and managed services. If someone else runs part of your infrastructure, ask them.
Security is ongoing work for us
GeoSolutions leads the development of MapStore and takes part in the security work of the GeoNode and GeoServer projects. When an issue is reported, we help analyse it, prepare and test the fixes, and coordinate the releases with the rest of the community. We are certified ISO 27001. We are doing our best to strengthen security in everything that we do.
How we can help
Running open source in production does not mean running it alone. With our Enterprise Support Services, Enterprise Subscription Services and Professional Training Services we help organisations:
- understand whether a security issue is relevant to their installation
- plan and apply upgrades
- review their deployments, including the web servers and proxies in front of them
- train their teams
Want to talk about your MapStore, GeoServer or GeoNode installation? Write to sales@geosolutionsgroup.com.
This post is general guidance on the products as published. It is not an assessment of any specific installation.
Sources
- NCSC: Critical security issue affecting PHP
- Help Net Security: PHP2Shell, critical PHP vulnerabilities patched
- CSA Singapore: Critical vulnerabilities in F5 NGINX products
- Beazley Security: NGINX Rift (CVE-2026-42945)